Provisioning MCP Tools
Your organization's MCP tools reach configured desktop tools automatically. While Configure agents from AgentPass is on, each tool with Provide MCP servers ticked receives the MCP servers your gateway publishes. A developer's tools then already list the tools your organization provides, with no setup on the desktop.
Provide MCP servers is a checkbox on each tool's card in Agent Configuration. It is ticked when you turn the tool on. Unticking it removes the MCP servers AgentPass added, and keeps the developer's own. Which servers the tools receive, you control per connector.
Turning on Provide MCP servers needs Settings: Edit, which Admin has. With Settings: View, which Operator and Auditor also have, you see it read-only. Publishing a connector to the catalog needs Connectors: Edit, which Admin has.
What Is Provisioned
The gateway provisions each managed tool with the same MCP servers it publishes to every agent:
- The HYPR AgentPass MCP server. The gateway's own server,
hyprmcp, gives an agent the approval, messaging and status tools described in The HYPR AgentPass MCP Tools. - Every enabled MCP-capable connector not excluded from the catalog. These are your MCP server connectors and REST API connectors, each reached through the gateway.
The workstation writes these servers into each managed tool's own MCP configuration, and merges them with servers the developer added. Claude Code, Claude Desktop, Codex and Cursor each keep theirs in a different place, listed in Configuration Locations.
The gateway holds the real credentials for the servers behind the connectors. The workstation stores only gateway addresses, never a provider secret.
Every managed tool receives the same list, because provisioning is per organization, not per tool.
The HYPR AgentPass MCP Tools
The hyprmcp server gives every agent these tools. The agent calls them itself, usually after a gateway response tells it to. A developer does not need to call them by hand.
| Tool | What the agent uses it for |
|---|---|
check_approval_status | Waits for a supervisor's decision on an approval the gateway asked for, such as a first connection or a policy that requires approval. It waits up to 20 seconds, then answers APPROVED, DENIED, RESPONDED (the supervisor replied with a comment), PENDING (still waiting, so call again), EXPIRED, NOT_FOUND, NOT_ISSUED or NONE_PENDING. Called without an approval ID, it returns what the agent is waiting on. A first connection's approval also returns the agent's messaging token |
check_mcp_oauth_status | Waits for the person to finish signing in to the service behind an MCP connector that uses OAuth. It waits up to 20 seconds, then answers APPROVED (retry the original request), PENDING, EXPIRED or FAILED |
list_available_mcp_servers | Lists the MCP servers the gateway publishes, with their addresses, the agent's sign-in state on each, and snippets to add them to Claude Code or Claude Desktop |
get_messages | Reads new messages from the agent's supervisor, using its messaging token |
send_message | Sends a message to the agent's supervisor, using its messaging token |
The approval and messaging tools need a person to answer, so a workload agent cannot use them. See Having Conversations with Your Agent for messaging from the supervisor's side.
How a Developer Signs In to a Provisioned Server
The provisioned configuration carries no credential. How a developer's tool authenticates depends on the connector.
| Connector | What the developer does |
|---|---|
| An MCP server connector with its credential stored on the connector | Nothing. The gateway injects the stored credential, and the tool connects immediately |
| An MCP server connector that uses OAuth | Signs in to the server behind the connector the first time the tool connects, as described in Connecting to a Gateway MCP Connector |
| A REST API connector | Presents a gateway-issued credential, so the tool must first be onboarded as an agent. See Onboarding Your Agent |
Control Which Connectors Are Provisioned
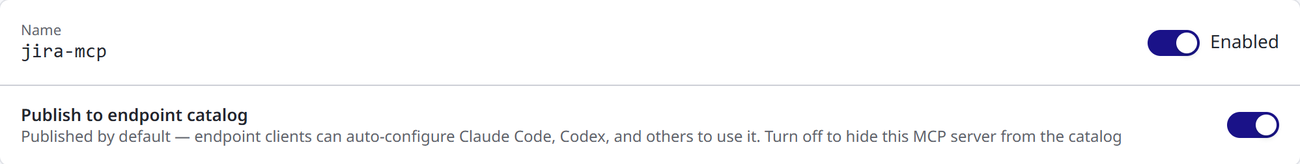
MCP provisioning follows the same catalog that decides which servers agents discover from the gateway. A connector's Publish to endpoint catalog switch, on its Overview tab, controls whether it reaches managed tools:
- The switch is on by default. An enabled, published connector is provisioned to managed tools.
- Turn it off to hide the connector from the catalog. It is then not provisioned to managed tools, and agents that ask the gateway which servers it publishes do not see it either.
There is no separate list of servers for desktop tools. The connectors your agents can discover are the connectors your managed tools receive.
New Connectors Appear Automatically
When you add a connector, or publish an existing one to the catalog again, it reaches your managed tools on their next check-in. No workstation needs any action.
Disabling a connector, or turning off Publish to endpoint catalog, removes it from managed tools on their next check-in. A desktop's Managed configuration confirms whether it applied its MCP configuration. See Managed Desktops.
Related
- Connectors — set up the connectors that expose MCP tools
- Connecting to a Gateway MCP Connector — how agents reach the MCP servers the gateway hosts, and how OAuth sign-in works
- Managed Desktops — confirm which tools have applied their MCP configuration