AWS Bedrock Mantle
Overview
An AWS Bedrock Mantle connector routes your developers' requests through HYPR AgentPass™ to Amazon Bedrock Mantle in your own AWS account. Use it for models served only on Mantle, such as Claude Mythos. Every request is subject to your policies and recorded in the Request Log.
You choose a region and name the AWS account the connector serves. AgentPass works out the Mantle endpoint from the region, unless you enter your own VPC endpoint. Developers keep their own AWS credentials: AgentPass stores none and adds none, and forwards each request with the developer's credential untouched.
Mantle has its own connector, separate from AWS Bedrock. Use the one that serves the models your developers need.
| Connector | Serves |
|---|---|
| AWS Bedrock | Models on the standard Bedrock runtime |
| AWS Bedrock Mantle | Models served only on Mantle, through the Anthropic Messages API and an OpenAI-compatible API |
The two connectors can exist side by side, and an organization can have one of each. In Observe only mode, a developer attributed the same way on both connectors is one agent, so turning that agent off stops their traffic on both. When Mantle attributes a request only to the AWS account, that account is the agent, and turning it off stops every developer in the account.
Before You Begin
Complete these tasks in the AWS console first. On the connector form, Set up in AWS opens the same steps, with your chosen region filled in and the policy ready to copy.
- Create an IAM policy from the following permission policy, replacing
<region>with your region. - Attach the policy to the permission set or role your developers sign in with. Nothing is granted to AgentPass.
- In Amazon Bedrock, open the region you will use and enable access to the models your developers need. Some models also need provider data sharing.
- If your organization uses service control policies (SCPs), allow
bedrock-mantle:CreateInference,bedrock-mantle:CountTokensandbedrock-mantle:CallWithBearerToken. - If you run AgentPass in your own AWS account, allow the AgentPass role
sts:GetAccessKeyInfo, so each request is attributed to the caller's AWS account. - Optional: to see developer names in the Request Log, set up identity enrichment. See Naming the developer behind a request.
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Sid": "AgentPassInvokeBedrockMantle",
      "Effect": "Allow",
      "Action": [
        "bedrock-mantle:CreateInference",
        "bedrock-mantle:CountTokens"
      ],
      "Resource": "arn:aws:bedrock-mantle:<region>:*:project/*"
    },
    {
      "Sid": "AgentPassBedrockMantleApiKeys",
      "Effect": "Allow",
      "Action": "bedrock-mantle:CallWithBearerToken",
      "Resource": "*"
    }
  ]
}
The second statement is needed only by developers who use a Bedrock API key.
Create the policy, and the optional identity role or IAM user, in the same AWS account you enter on the connector. A credential from any other account is refused.
Create the Connector
- In the console, open Connectors, and click Add connector.
- Choose AWS Bedrock Mantle.
- Complete the fields described in the following table.
- Click Test connection. See Test the connection.
- Click Next.
- Choose the onboarding mode. See Onboarding new developers.
- Click Create Connector.
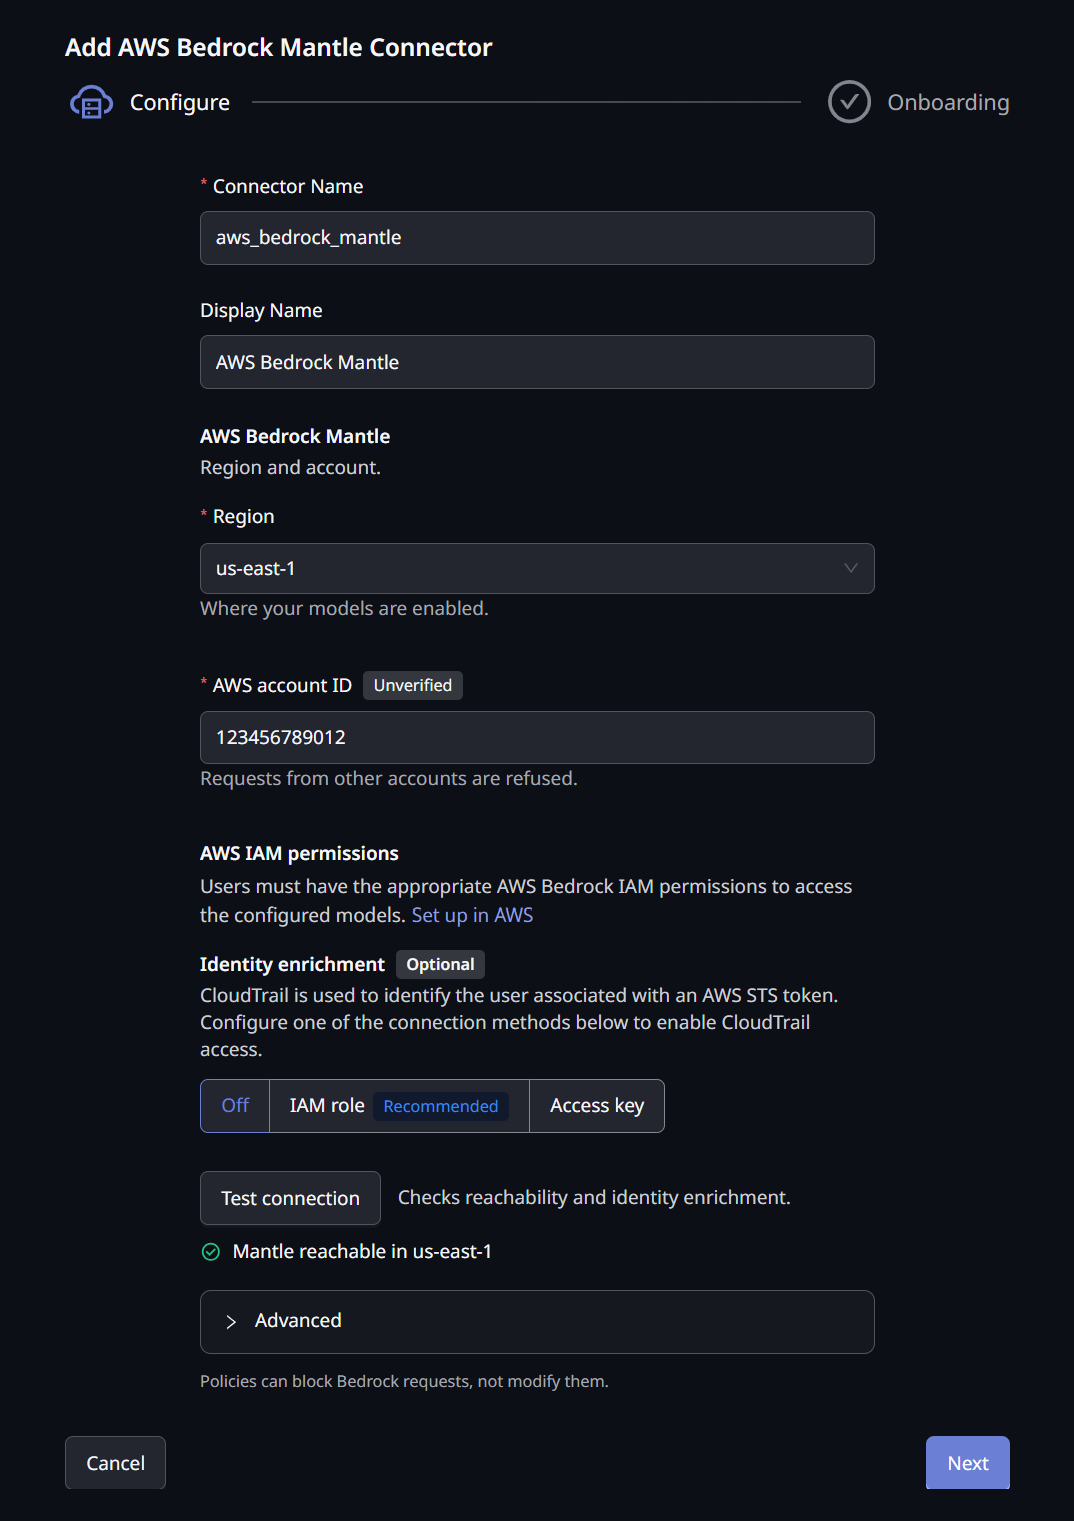
The connector form has these fields.
| Field | Description |
|---|---|
| Connector Name | The internal name for this connector |
| Display Name | The name shown in the console |
| Region | The AWS region your Mantle models run in. Model availability differs by region, so use the region where you enabled model access |
| AWS account ID | The 12-digit account your developers sign in to. Requests signed by any other AWS account are refused |
| Identity enrichment | Optional. Off, IAM role or Access key. Lets the Request Log name developers, and is needed for Require Approval. See Naming the developer behind a request |
There is no authentication field. The connector accepts the AWS credential each developer brings.
The Advanced section holds two optional settings:
- A VPC endpoint, for a network that reaches Mantle through your own VPC endpoint. See Private connectivity.
- The identification rate limits, which work as they do on the AWS Bedrock connector.
An organization has one Mantle connector. To change the account or region, edit the existing connector. The China and AWS GovCloud (US) regions are not available.
Test the Connection
Test connection works before the connector is saved. It reports a checklist, one row per check.
| Row | Meaning |
|---|---|
| Mantle reachable in region | The gateway reached Mantle in the chosen region |
| Mantle reachable via VPC endpoint | The gateway reached Mantle through the VPC endpoint you entered |
| Identity enrichment working | The identity role or access key can read CloudTrail |
| This deployment has no AWS identity | AgentPass has no AWS identity that a trust policy can name, so it cannot assume a role here. Use an access key instead |
| Can't assume the role | AWS refused to let AgentPass assume the role. See Troubleshooting |
| Can't read CloudTrail in region | The role or key lacks the caller-identity permission for that region |
| Couldn't check identity enrichment | AWS did not answer the check, for example because it was busy. Run the test again |
| Account matches | The identity credential belongs to the account you entered |
| Credential is from another account | The identity credential belongs to a different account. Correct the account ID, or use a credential from the account you entered |
| Account not verified | Nothing confirmed the account yet. Saving is allowed, and the first successful request confirms it |
The identity rows appear only when identity enrichment is on. A failed identity row carries a Fix in AWS setup link, which opens the AWS setup steps for the role or IAM user.
When an identity check fails, the error AWS returned appears under the row, word for word. It names what AWS refused, such as the role and the principal that tried to assume it, or the missing permission, so you can correct the policy AWS points to.
Connect Your Developers
Once the connector exists, its page shows a Connect AI tools card with the settings to give your developers. The values are filled in for your gateway, region and account. The card has three steps: configure the tool, authenticate with AWS, and verify the connection.
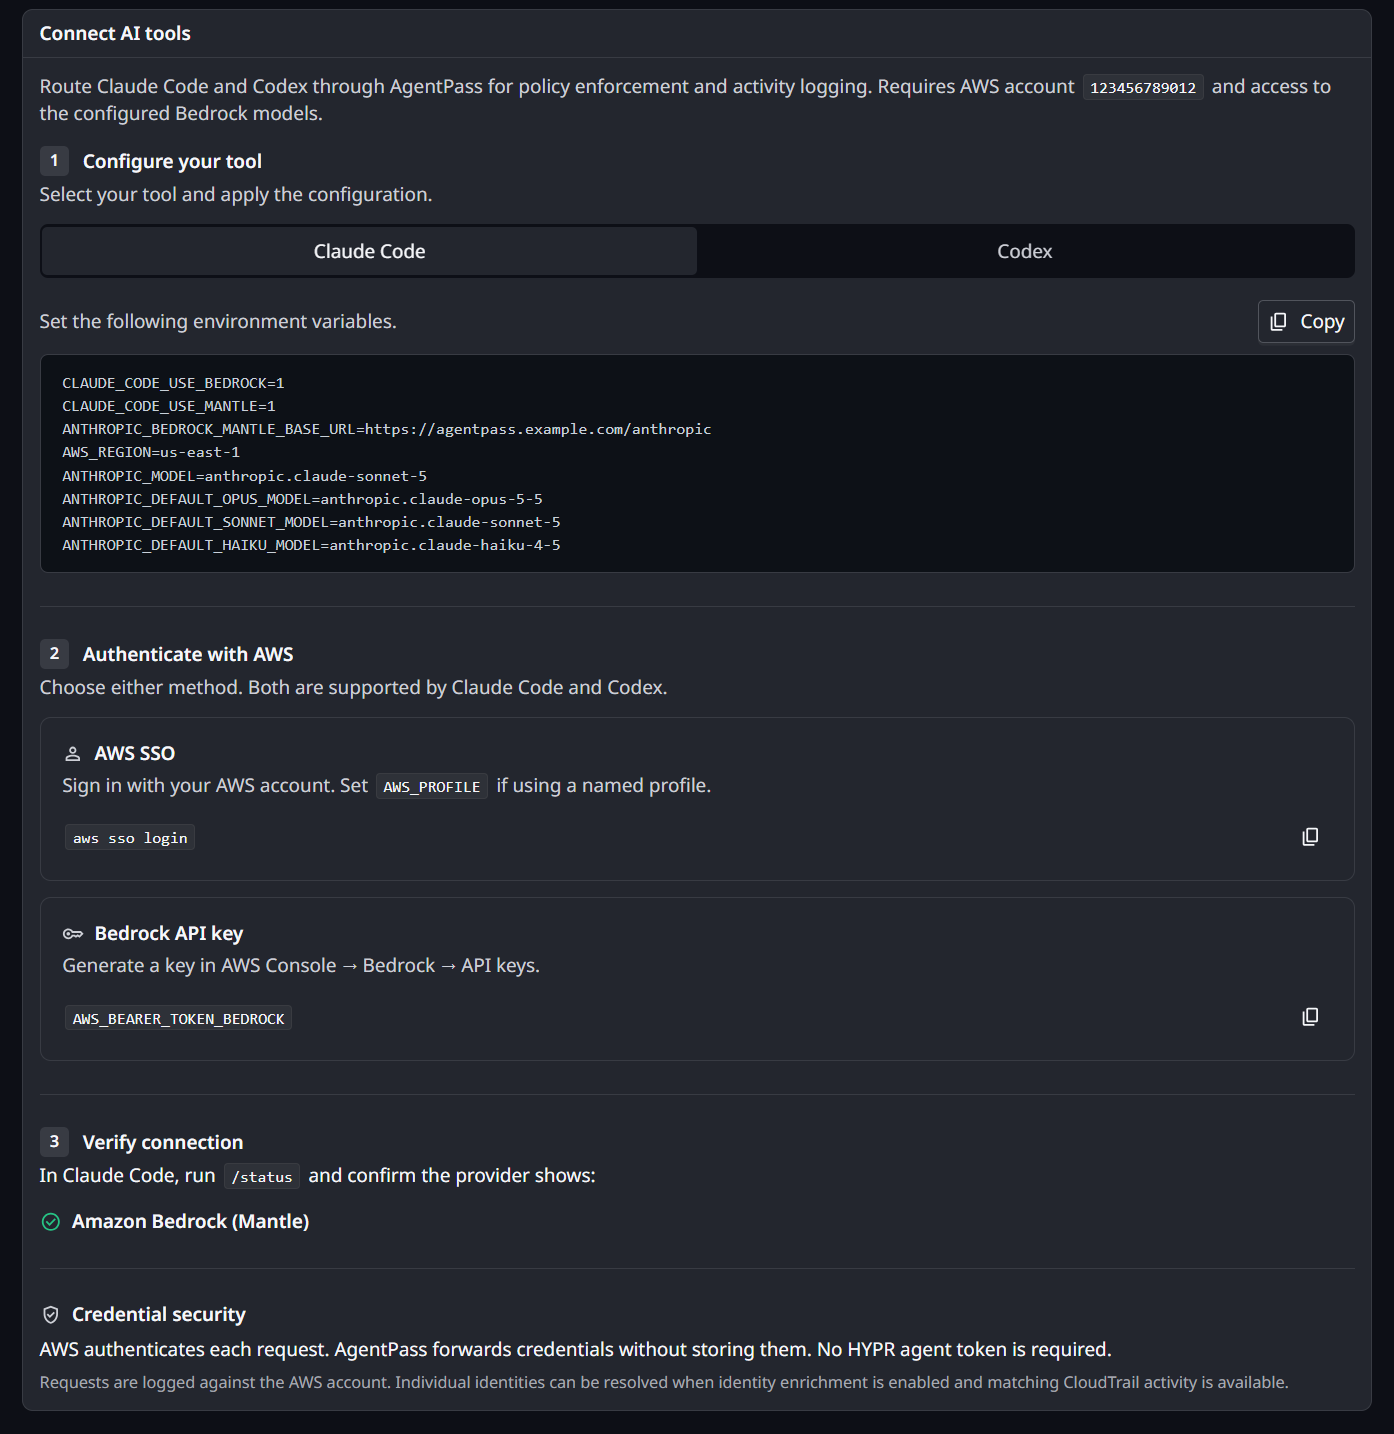
Configure the Tool
For Claude Code, the developer sets these environment variables, using the values on the card:
CLAUDE_CODE_USE_BEDROCK=1
CLAUDE_CODE_USE_MANTLE=1
ANTHROPIC_BEDROCK_MANTLE_BASE_URL=<your gateway URL>/anthropic
AWS_REGION=<your region>
The card also pins model IDs in ANTHROPIC_MODEL and the ANTHROPIC_DEFAULT_*_MODEL variables. Use models your AWS account has access to.
For Codex, the developer adds this to ~/.codex/config.toml, and changes profile if they use a named AWS profile:
model_provider = "amazon-bedrock"
model = "<a model ID from the card>"

[model_providers.amazon-bedrock]
base_url = "<your gateway URL>/openai/v1"

[model_providers.amazon-bedrock.aws]
region = "<your region>"
wire_api = "responses"
profile = "default"
Authenticate With AWS
Each developer authenticates in either of two ways. Both work in Claude Code and in Codex, and a developer can switch between them at any time.
- An AWS SSO session. The developer runs
aws sso loginas usual, and setsAWS_PROFILEif they use a named profile. - Their own Bedrock API key. The developer creates a key in the AWS console, under Bedrock → API keys, and sets
AWS_BEARER_TOKEN_BEDROCK.
No HYPR agent token is needed. AWS authenticates every call from the developer's own credential, and authorizes it against their own permissions. AgentPass forwards the credential without storing it.
Verify the Connection
The developer starts their tool and runs /status:
- In Claude Code, the provider shows Amazon Bedrock (Mantle).
- In Codex, the model provider shows
amazon-bedrock, and the base URL is your AgentPass gateway address.
Tell your developers which AWS account the connector serves. A credential from any other account is refused, and AWS's own error does not say which account was expected. The card names the account for you.
Onboarding New Developers
The connector's onboarding mode decides what happens the first time a developer reaches Mantle through the gateway. You choose it on the create form's last step, and can change it later on the connector page's Onboarding Mode card. See Onboarding Mode.
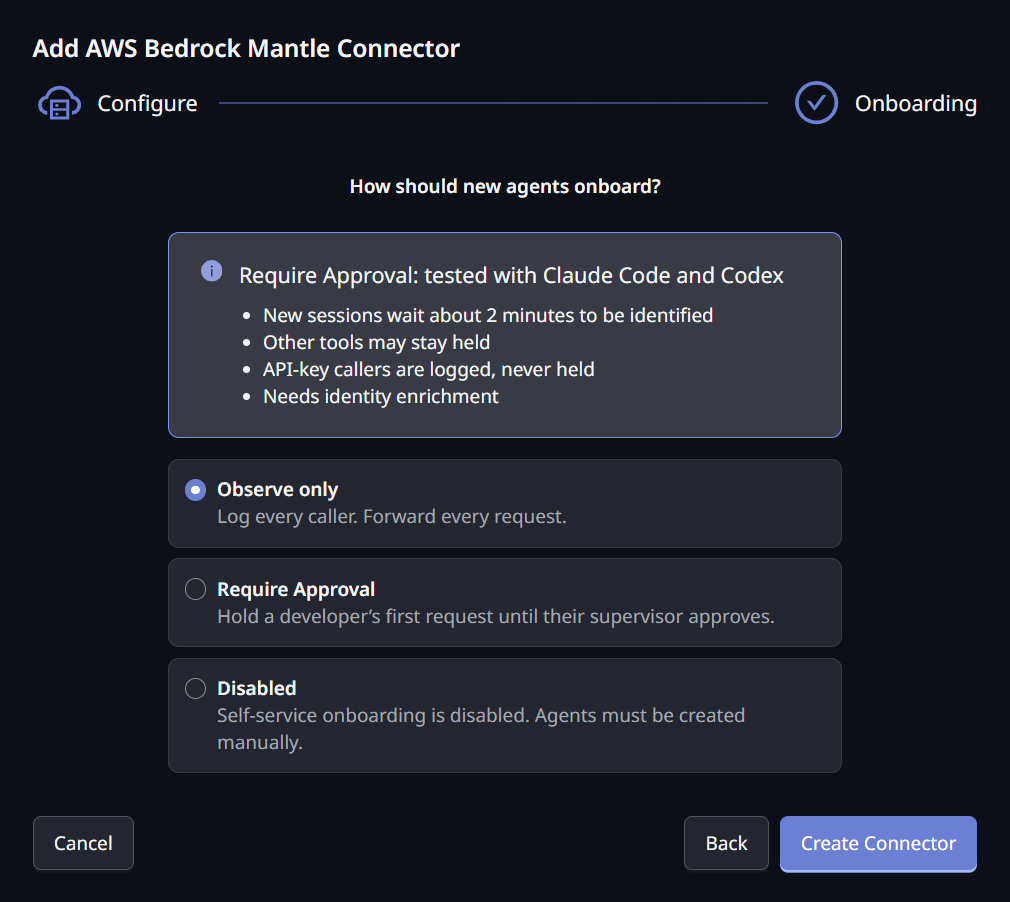
| Mode | What happens on a developer's first request |
|---|---|
| Observe only (the default) | The request is forwarded, and the caller is recorded |
| Require Approval | A developer signing in with AWS SSO is held until their supervisor approves them. Once approved, their traffic flows normally |
| Disabled | Self-service onboarding is off |
Require Approval uses the same supervisor handshake as your other connectors. See Onboarding Your Agent for the supervisor's side.
You cannot save a connector in Require Approval without identity enrichment. On the Onboarding Mode card, Require Approval stays unavailable until the connector has it, with the hint Needs identity enrichment. Add it in Edit. Approval is per developer, and identity enrichment is what lets the gateway name one.
What to Expect With Require Approval
Require Approval on Mantle is tested with Claude Code and Codex. Keep these points in mind before you switch it on:
- New sessions wait about 2 minutes to be identified. A developer who has just signed in to AWS is asked to retry until AgentPass can name them.
- Other tools may stay held. AgentPass names a developer from AWS activity their tool records at startup. Claude Code and Codex both do this. A tool that makes no other AWS call, such as a script calling the API directly, is never named, so it stays held.
- API-key callers are recorded, never held. A Bedrock API key belongs to an AWS account, not a person.
Until the developer is named, their tool shows:
AgentPass is still identifying you — new AWS sessions take about 2 minutes.

Try again in 2 minutes. Claude Code and Codex are recognised; other tools may not be. Still blocked? Ask your administrator.
Nothing is sent to Mantle while a developer waits. Once they are named, their approval is raised as normal.
Attribution and the Request Log
Mantle traffic appears in the Request Log alongside your other connectors, with the model name and token counts. Each row opens the same AWS caller details as an AWS Bedrock request.
Requests are attributed to the AWS account the credential belongs to. A long-term Bedrock API key always names its IAM user.
Naming the Developer Behind a Request
To see developer names instead of AWS account IDs, turn on identity enrichment. It works the same way as on the AWS Bedrock connector: you choose an IAM role, which is recommended, or an Access key, and the console walks you through creating it. See Naming the developer behind a request for both routes.
Your organization has one external ID for identity roles, so one role can serve both your Bedrock connectors. If your AWS Bedrock connector already uses a role, choose Use the role from your other Bedrock connector on the Mantle form. When AgentPass has no AWS identity to name in a trust policy, the IAM role option is unavailable, and hovering over it shows why; use an access key instead.
If identity enrichment stops working, the connector's page shows Identity enrichment failing since a time, with the check to make. See When identity enrichment fails.
With identity enrichment on, a developer is named once their AWS session has made another AWS call that CloudTrail records. Claude Code and Codex both make one at startup. Until then, their requests are attributed to their AWS account.
Policies on Mantle Traffic
Your AgentPass policies apply to every Mantle request, whichever credential the developer brought. Lead a Mantle-specific rule with a template guard:
connector.template == "AWS_BEDROCK_MANTLE"
The Bedrock caller attributes are filled in for Mantle requests as well. Mantle adds connector.aws.bedrock.project, the Bedrock project the request runs in.
Mantle model IDs carry no version or region prefix, for example anthropic.claude-mythos-5. A rule written for standard Bedrock model IDs does not match them, so write Mantle rules against Mantle IDs.
A developer's AWS signature covers the exact request they sent. A pre-request policy that rewrites a Mantle request invalidates that signature, and AWS then refuses it. Policies that inspect and deny work normally.
Private Connectivity
The gateway can reach Mantle privately, through an interface VPC endpoint for Bedrock Mantle (com.amazonaws.<region>.bedrock-mantle) in your AWS account. Pick the route by the names your network resolves.
The following table compares the two routes.
| Route | Use it when | On the connector |
|---|---|---|
| Private DNS | The endpoint has private DNS enabled, and the gateway resolves bedrock-mantle.<region>.api.aws to it | Nothing to configure |
| The endpoint's DNS name | Your network resolves only amazonaws.com names | Enter the name in VPC endpoint |
Entering a VPC Endpoint
Enter the endpoint's DNS name when your network can't resolve Mantle's public api.aws name.
- In the AWS console, open the VPC endpoint, and copy its DNS name from the Details tab. Use the regional name, the one without an Availability Zone in it.
- On the connector form, expand Advanced.
- Paste the name into VPC endpoint.
- Click Test connection. The checklist shows Mantle reachable via VPC endpoint.
- Finish creating the connector, or click Save on an existing one.
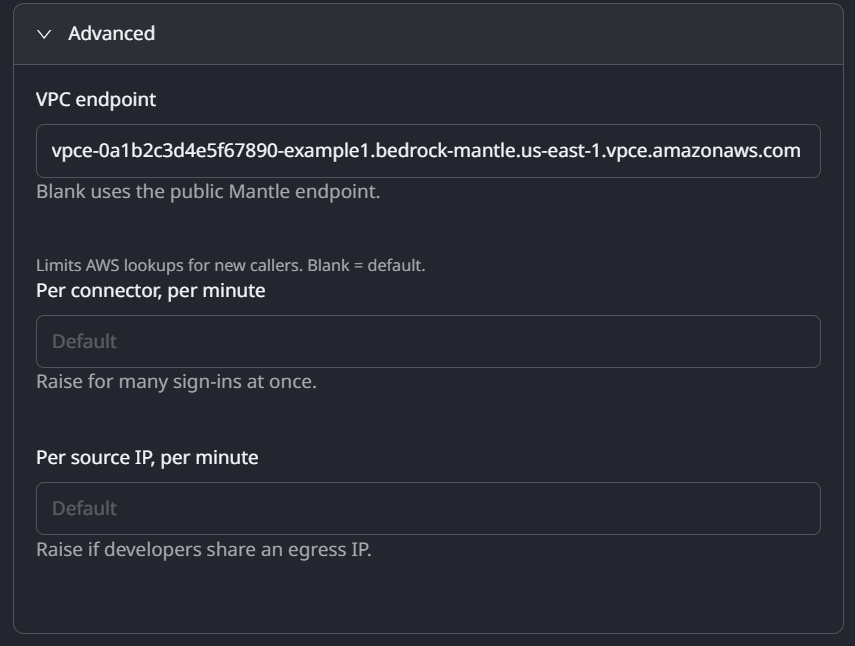
The gateway then sends Test connection and every developer request to the endpoint. Developers change nothing: their tools still point at AgentPass. To return to the public Mantle endpoint, clear the field.
The field accepts a Bedrock Mantle hostname under amazonaws.com or api.aws. A URL, an IP address or any other name is refused when you save.
Mantle's certificate covers its public api.aws name and the endpoint's own vpce DNS names. Another name that your DNS points at the endpoint, such as a record in your own private zone, fails the TLS check.
The field needs private network access for your organization. Until it is enabled, the field is unavailable and reads Private network access isn't enabled for this tenant. On HYPR-hosted AgentPass, ask HYPR support to enable it. See Allow a private network address.
Troubleshooting
Start with the symptom you see.
| What you see | What to check |
|---|---|
| Test connection cannot reach Mantle | Confirm the region is one where Mantle is available, and that your network permits outbound access |
| Couldn't reach … the hostname doesn't resolve | The gateway's DNS can't resolve the name. For the public api.aws name, use one of the private connectivity routes. For a vpce name, check that you copied all of it |
| Couldn't reach … the connection was refused, or the connection timed out | The name resolves, but the network blocks the connection. Check the route to the endpoint, its security group allows TCP 443 from the gateway, and any firewall in between |
| Couldn't reach … the TLS handshake failed | A proxy is inspecting TLS, or the name is not the endpoint's own DNS name. See Private connectivity |
| isn't an AWS Bedrock Mantle hostname | Enter the endpoint's DNS name on its own, without https:// or a path |
| Private network access isn't enabled for this tenant | Ask HYPR support to enable private network access for your organization |
| The connector will not save, reporting another Mantle connector | An organization has one Mantle connector. Edit the existing one |
| The connector will not save in Require Approval | Require Approval needs identity enrichment. Add an IAM role or an access key, or use Observe only |
| Can't assume the role | Read the error AWS returned under the row: it names the role and the principal AWS refused. Recreate the role's trust policy from Set up role in AWS, and confirm the role is in the account the connector serves |
| Couldn't check identity enrichment | AWS did not answer the check. Run Test connection again |
| Can't read CloudTrail in region | Attach the caller-identity permission policy from the setup steps to the role or IAM user |
403 with AccessDenied | The credential is valid, but lacks permission. Confirm the permission policy is attached, the SCPs allow the three Mantle actions, and model access is enabled in that region |
| Codex requests fail | Confirm base_url ends in /openai/v1 |
| A developer is told AgentPass is still identifying them | Expected for about 2 minutes after each new AWS sign-in on a Require Approval connector. See What to expect with Require Approval |
| A developer stays held well past 2 minutes | Their tool may make no AWS call that CloudTrail records. Use Claude Code or Codex, or switch the connector to Observe only. If every developer is held, run Test connection to check identity enrichment |
| The Request Log shows an AWS account but no developer name | Identity enrichment is off, or the developer's session has not yet made an AWS call that CloudTrail records |
| Identity enrichment failing since … on the connector page | The role can't be assumed, or the role or key can't read CloudTrail. Follow the check the warning names, then run Test connection |
Related
- AWS Bedrock — the connector for the standard Bedrock runtime
- Onboarding Mode — what each mode does on every connector
- Connectors — the other kinds of connectors you can add
- Bedrock Caller Policies — govern Bedrock and Mantle traffic by the developer behind it
- Viewing the Request Log — read the traffic this connector produces