Identity and Token Model
Every request the HYPR AgentPass™ gateway forwards carries one of three identities. The identity tells you who is accountable for the request, and what it can reach.
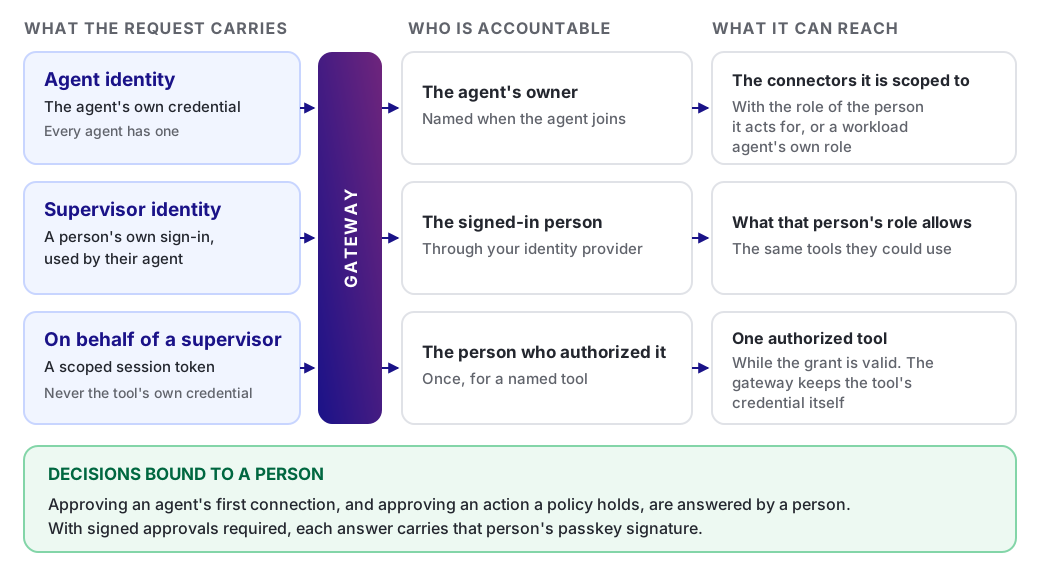
The following table summarizes what each identity proves.
| Identity | What it proves |
|---|---|
| Agent identity | The request came from a specific, named agent, with a person accountable for it |
| Supervisor identity | The person signed in to AgentPass is the one behind the agent |
| On behalf of a supervisor | A person authorized the agent to act for them on one named tool, for a bounded time |
Agent Identity
An agent is an identity in its own right, not a property of a person. AgentPass gives it a credential of its own, and records its owner.
-
When it is created. An agent gets its identity when it is imported, when it is created in AgentPass, or when it first connects.
-
Who is accountable. Every agent has an owner. A workload agent, which runs with nobody at the keyboard, gets its accountable owner when it is created.
-
What it reaches. The connectors the agent is scoped to, with the tools a role permits. That role belongs to the person the agent acts for: its owner, or the person chatting with it. A workload agent uses a role of its own.
-
Where to manage it. See Agent Identity.
For a workload agent, the owner and the authority are separate. The owner answers for the agent, and its own role decides what it may do. It uses its owner's connected accounts only on a connector an administrator names. See The Accountable Owner.
Every agent is also described by where it runs, and whose access it uses. See How AgentPass Organizes Agents.
Supervisor Identity
A supervisor signs in to AgentPass through your identity provider. An agent can then act with that identity directly. For example, a coding agent on the supervisor's own workstation signs in to a connector as that supervisor.
-
Who is accountable. The request is attributed to the signed-in supervisor.
-
What it reaches. The supervisor's role decides which tools the agent is offered, and which it may call.
-
Where to manage it. See Supervisor Identity.
Roles arrive from your identity provider, or are assigned in the console. See Roles and Permissions.
On Behalf of a Supervisor
Some tools are protected by their own sign-in. For those, the agent never holds the tool's credential:
-
The supervisor authorizes the connection once.
-
The gateway stores the resulting credential.
-
The agent receives a scoped session token, good for that tool and nothing else.
Revoking the grant, or letting it expire, cuts the agent off. The supervisor's own access is untouched.
See Acting on Behalf of a Supervisor.
Decisions Bound to a Person
Two decisions on the request path are made by a person, and bound to them:
-
Approving an agent's first connection
-
Approving an action a policy holds
Both are answered on the HYPR mobile app or in the console, and the record shows who answered.
With Require signed approvals set to Required (production), every approval carries the supervisor's passkey signature. The record then proves which person approved which action. A denial needs no passkey. To set this up, see Connecting to Your HYPR Tenant.
Related
-
Identity — configure each identity
-
Architecture: The Request Path — where identity sits on the path
-
Approving and Denying Agent Actions — what a passkey-bound approval looks like to the supervisor