Request Log
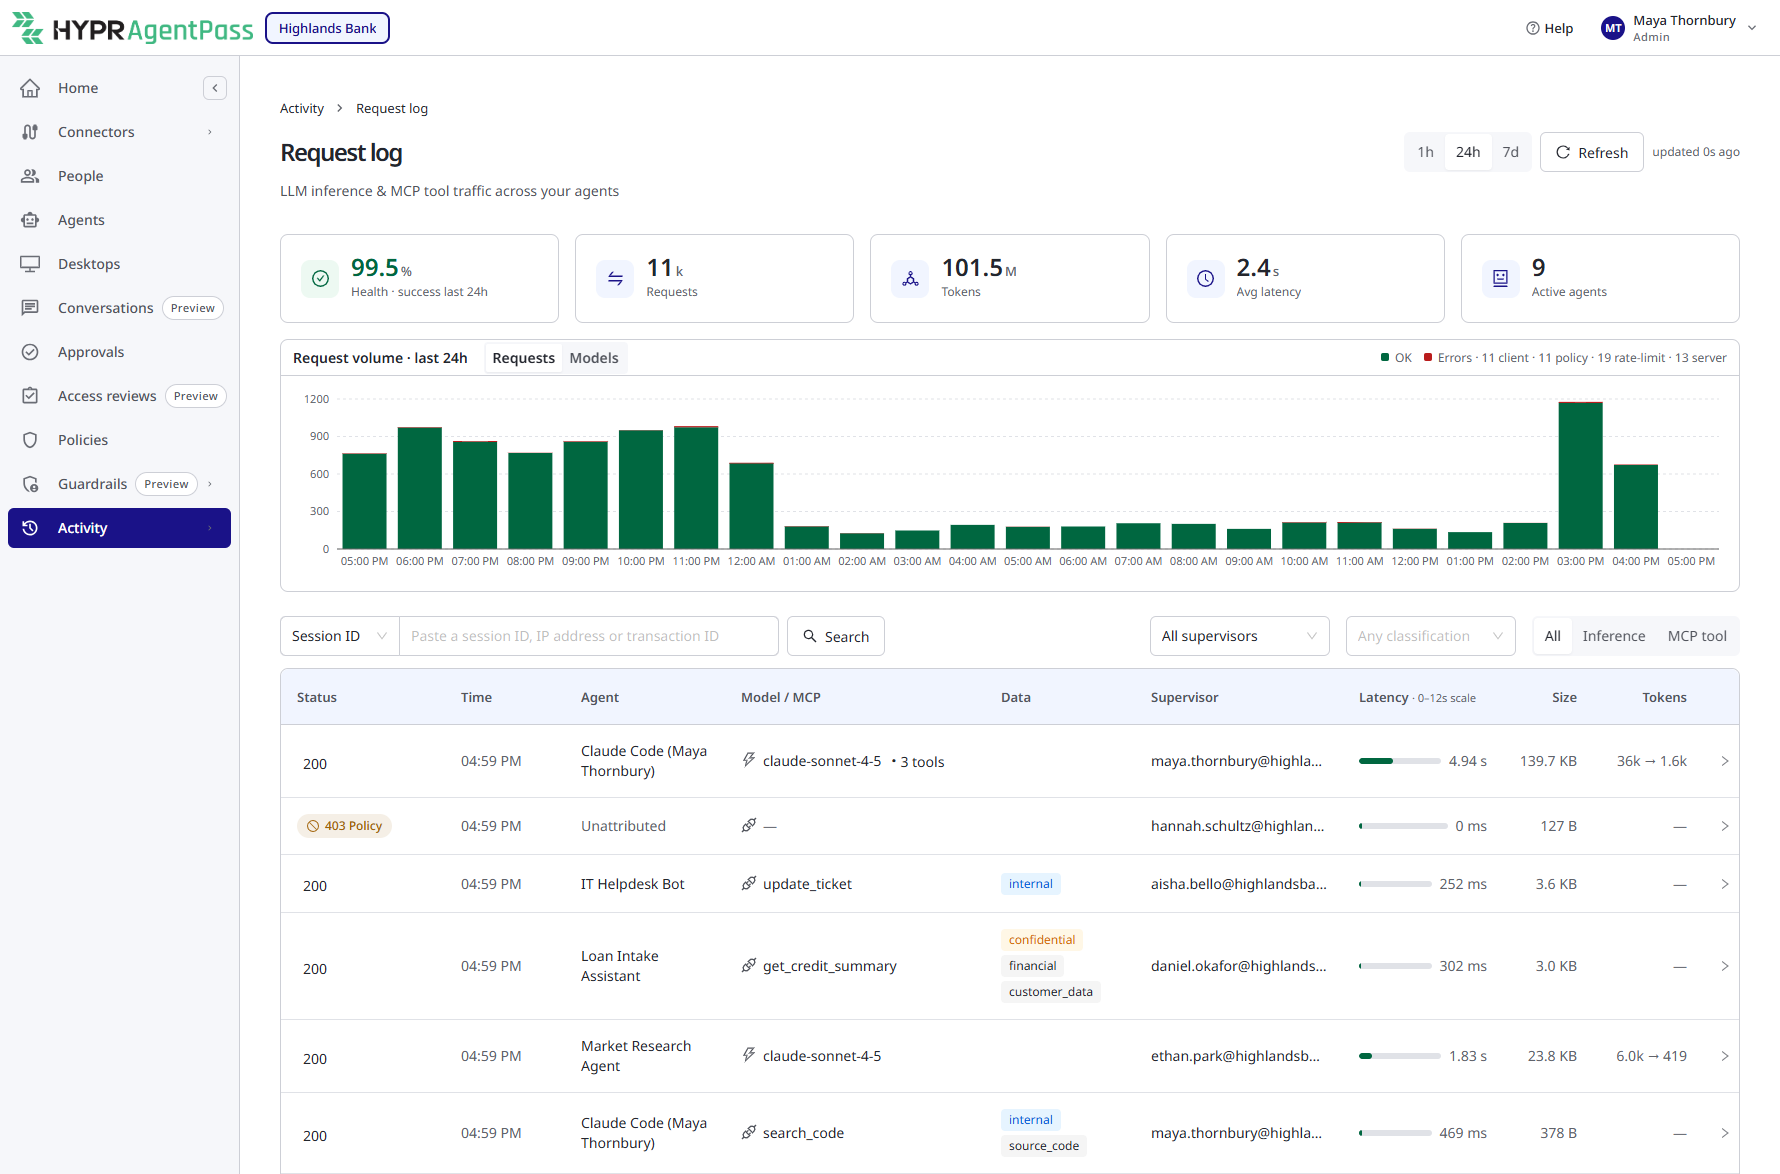
The Request log lists the traffic your agents send through HYPR AgentPass™: every inference call to a language model, and every MCP tool call. Each request is attributed to the agent that made it and to that agent's supervisor. Open it from Activity › Request log.
This page is the reference for the whole page, for every role that can open it. For a supervisor's view of the page, and a closer look at one request, see Viewing the Request Log.
Who Sees What
You need Request log: View to open the page. Its scope decides whose requests you see, on every part of the page. See Permissions by Role.
| Scope | Requests shown | Built-in roles with this scope |
|---|---|---|
| All | Every supervisor's requests | Admin, Operator, Security analyst, Auditor and Model governance owner |
| Own | Requests from the agents you supervise | Supervisor |
The filters follow your permissions:
- Type is available to everyone who can open the page.
- Supervisor appears for every role with the All scope.
- Classification appears for a role that holds Data labels: View, and only when your organization has classification tiers. Admin, Operator, Security analyst and Auditor hold it.
The Page Header
The header sets what the rest of the page covers:
- Time range. 1h, 24h or 7d. The default is 24h. The range applies to the summary cards, the chart, the stream and the supervisor filter.
- Refresh. Fetches the latest activity, and returns the stream to its first page. The page does not refresh itself.
- Updated. How long ago the page last fetched its data.
The time range reaches back up to 7 days. How long each category of event is kept is shown on Data Management. A request older than the time range can still be opened from a policy decision that links to it. See Open a Request from a Policy Decision.
Summary Cards
Five cards summarize the time range. Hover over a card for its breakdown.
| Card | Shows | On hover |
|---|---|---|
| Health | The share of requests that succeeded. The label names the time range, such as success last 24h | How many of all requests succeeded |
| Requests | The number of requests | Inference calls and tool calls, separately |
| Tokens | Input and output tokens together | Input and output tokens, separately |
| Avg latency | The average latency | Average across all requests |
| Active agents | The number of distinct agents that sent traffic | How many requests carried no agent identity, or All requests attributed |
The cards follow the time range only. The stream filters do not change them.
Request Volume
Request volume plots the requests in the time range over time. Switch the view between Requests, which separates successes from errors, and Models, which stacks inference calls by model. A model the gateway could not identify shows as Unknown.
Like the summary cards, the chart ignores the stream filters.
Request Stream
The request stream lists individual requests, newest first. It loads 50 at a time. Load more, at the end of the list, fetches the next set.

Filter the Stream
These filters narrow the stream. Each one returns the stream to its first page.
| Filter | Options |
|---|---|
| Type | All, Inference or MCP tool |
| Classification | Any classification, or one of your organization's tiers |
| Supervisor | All supervisors, or one supervisor. The list is searchable |
The classification filter matches the tier a call carried when it was made. See Data Classification.
Search the Stream
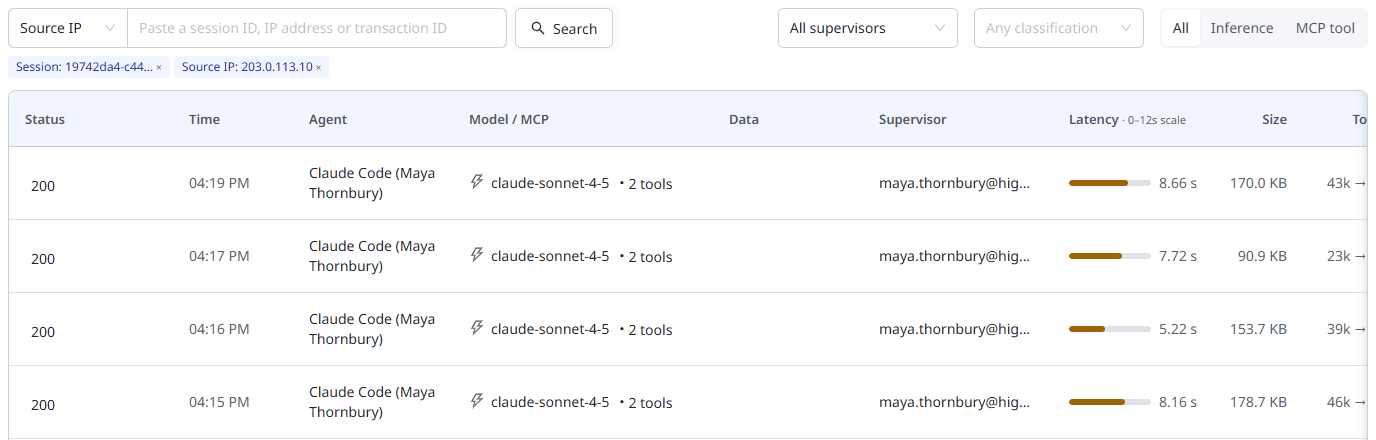
The search, at the left of the row above the stream, narrows it to one coding session, one source IP or one transaction. Choose what to search by, paste the value, and click Search.
| Search by | The value to paste |
|---|---|
| Session ID | The identifier a coding agent sends with each request. A request's detail panel shows it under Coding session |
| Source IP | An IPv4 or IPv6 address. See Where the Source IP Comes From. An IPv6 address matches however it is written, such as 2001:db8::1 or 2001:DB8:0:0:0:0:0:1 |
| Transaction ID | The txn value of an exported event. See What an Exported Event Carries |
A search matches the whole value, not part of it. Each active search shows as a chip above the stream, such as Source IP: 203.0.113.10. A chip shortens a long session or transaction ID. Hover over the chip to read the whole value, and click its × to remove that search.
Searches combine. With a session and a source IP both set, the stream lists only that session's requests from that address. They also combine with the type, classification and supervisor filters, and cover the time range in the header. Like the filters, a search narrows the stream only. A search never shows requests your role cannot otherwise see.
When nothing matches, the stream reads No requests match this search in the selected time range. Widen the time range, or remove a chip. A value that is not well formed is not searched, and a message under the search box says why:
- Session ID is not valid.
- Enter an IPv4 or IPv6 address.
- Transaction ID is not valid.
Link to a Search
The search and the time range are part of the page's address. A reload keeps them, and a link opens the Request log already searched. Build a link from an alert in your SIEM, for example, to open the requests behind it.
https://gateway.example.com/admin/ui/request-log?clientIp=203.0.113.7&range=7d
| Parameter | Value |
|---|---|
session | A session ID |
clientIp | An IPv4 or IPv6 address |
txn | A transaction ID |
range | 1h, 24h or 7d. Without it, or with any other value, the time range is 24h |
Join parameters with &, such as ?session=<session ID>&clientIp=203.0.113.7, and URL-encode each value. Everyone who opens the link sees only the requests their role allows.
Columns
Each row shows these columns, from left to right.
| Column | What it shows |
|---|---|
| Status | The status code. A request that did not succeed also shows its category. See the following table |
| Time | The time of day for today's requests, otherwise the date and time. Hover for the full timestamp |
| Agent | The agent's name, or Unattributed. An AWS Bedrock or AWS Bedrock Mantle request adds an icon that opens its AWS caller details. See AWS Bedrock |
| Model / MCP | The model, or the MCP tool or method. An inference call that asked for tools adds how many |
| Data | The classification tier and tags the call carried |
| Supervisor | The supervisor responsible for the agent |
| Latency | A bar on a 0 to 12 second scale, with the value. Hover for model and gateway time |
| Size | The size of the request |
| Tokens | Input and output tokens |
The status category tells you how a request ended.
| Category | Status |
|---|---|
| Policy | 403 |
| Rate limit | 429 |
| Timeout | 504 |
| Server | Any other 5xx status |
| Client | Any other 4xx status |
| Redirect | A 3xx status |
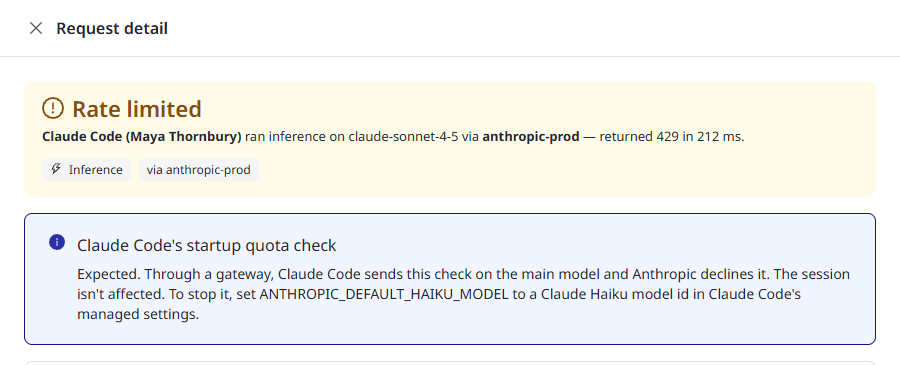
A small Claude Code request with a 429 status and an info icon is Claude Code's startup quota check. Through a gateway, Claude Code sends it on its main model and Anthropic declines it. The session is not affected. To stop it, set ANTHROPIC_DEFAULT_HAIKU_MODEL to a Claude Haiku model ID in Claude Code's managed settings. The request's detail says the same.
Request Detail
Click a row to open Request detail. The row stays highlighted while the panel is open.
The panel opens with how the request ended, such as Succeeded, Blocked by policy or Timed out. It then shows:
- The latency, time to first byte, gateway time, tokens and payload size
- A What happened timeline
- The call's data classification, and what its session had already read, when they apply. Markers show whether the session had a Sensitive read, read from an Untrusted source or met Hostile content
- The spend decision, when a spend limit held or stopped the request: what had been spent against the limit, the policy, the message sent to the agent, and who the request is waiting on. A held request is listed with status 202, as Awaiting approval
- The source IP the request came from. See Source IP
- The coding session the request belongs to, when the agent reported one
- The tool calls the model requested
- The captured Request and Response, with their headers and bodies, and the whole body behind a cut one when your deployment keeps it
- What the upstream returned, when it differs from what the gateway returned
- The supervisor responsible for the agent, as Supervised by
For what each part shows, and how to read the captured bodies, see Inspect a Single Request.
Source IP
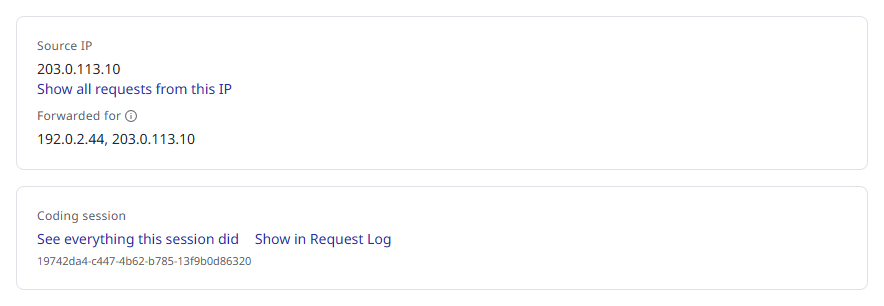
The Source IP card shows the address the request came from. Show all requests from this IP opens the Request Log searched by that address. Not recorded means the gateway holds no source IP for the request, such as a request recorded by an earlier gateway version.
Forwarded for appears below it when the request arrived with a forwarding chain that holds more than the source IP. It is the request's X-Forwarded-For header, as the gateway received it. Its tooltip reads Sent by the client and any proxies. Only the address your load balancer added is trusted. The client, or a proxy on the client's side, wrote every other address in the chain. Read it for context, and search by the Source IP.
The Coding session card adds Show in Request Log, which opens the Request Log searched by that session. Both links open at the 24h time range.
Where the Source IP Comes From
A request's source IP is the address that connected to your load balancer: the client's machine, or the last proxy or network address translation device on the client's network. Addresses that the client or its proxies wrote into the X-Forwarded-For header never become the source IP. The gateway keeps them as Forwarded for.
Your exports carry it too: every event a request causes carries that request's source IP. See What an Exported Event Carries.
The gateway is set up for the proxies in front of it. If you add a reverse proxy or another load balancer in front of the gateway, tell your HYPR representative, so the source IP stays the address your load balancer saw.
Open a Request From a Policy Decision
A policy decision links to the request that caused it. Following that link opens the Request Log with the request's detail panel already open. It opens even when the request falls outside the current time range. Closing the panel returns you to the stream.
See Investigating a Policy Decision.
When Export Files Stop Being Written
A role that holds Data retention: View sees a banner on this page when a gateway node cannot write its export files. The banner reads Event export files are not being written, and names the cause. It also gives the number of failed writes, how many nodes are affected and when the failures started.
Requests still reach the Request Log while the banner shows. The export files you collect for the same period are missing records. Check the export directory on the affected gateway nodes, including its free disk space and write permissions.
The banner clears once the node writes its export files again. It also appears on the Data Management page.
Related
- Viewing the Request Log — the supervisor's view, and how to read one request in depth
- Home — tiles, approvals and top lists across the gateway
- Data Management — what the gateway records, where it is sent, and how to send it to your SIEM
- Agent Session Forensics: Overview — read a coding agent's whole session instead of one request