Provisioning MCP Tools
Overview
Your organization's MCP tools reach managed desktop tools automatically. When you turn managed mode on, each managed tool is provisioned with the MCP servers your gateway publishes. A developer's tools then already list the tools your organization provides, with no setup on the workstation.
There is nothing to configure in the Desktop Tools view for this. You control it per connector.
Choosing which connectors are exposed is an administrator task, and needs permission to view and edit settings.
What Is Provisioned
The gateway provisions each managed tool with the same MCP servers it publishes to every agent:
- The HYPR AgentPass MCP server. The gateway's own server gives an agent the approval, messaging and status tools described in Connecting to a Gateway MCP Connector.
- Every enabled MCP-capable connector not excluded from the catalog. These are your MCP server connectors and REST API connectors, each reached through the gateway.
The workstation writes these servers into each managed tool's own MCP configuration, and merges them with servers the developer added. Claude Code, Claude Desktop, Codex and Cursor each keep theirs in a different place, listed in Configuration Locations.
The gateway holds the real credentials for the servers behind the connectors. The workstation stores only gateway addresses, never a provider secret.
Every managed tool receives the same list, because provisioning is per organization, not per tool.
How a Developer Signs In to a Provisioned Server
The provisioned configuration carries no credential. How a developer's tool authenticates depends on the connector.
| Connector | What the developer does |
|---|---|
| An MCP server connector with its credential stored on the connector | Nothing. The gateway injects the stored credential, and the tool connects immediately |
| An MCP server connector that uses OAuth | Signs in to the server behind the connector the first time the tool connects, as described in Connecting to a Gateway MCP Connector |
| A REST API connector | Presents a gateway-issued credential, so the tool must first be onboarded as an agent. See Onboarding Your Agent |
Control Which Connectors Are Provisioned
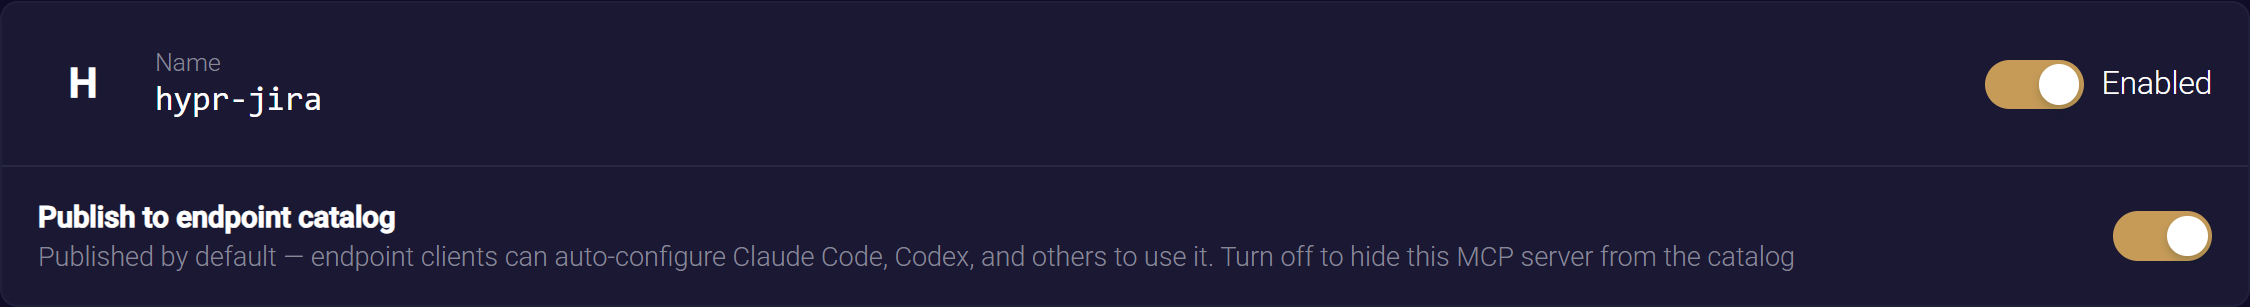
MCP provisioning follows the same catalog that decides which servers agents discover from the gateway. A connector's Publish to endpoint catalog switch, on its Overview tab, controls whether it reaches managed tools:
- The switch is on by default. An enabled, published connector is provisioned to managed tools.
- Turn it off to hide the connector from the catalog. It is then not provisioned to managed tools, and agents that ask the gateway which servers it publishes do not see it either.
There is no separate switch for desktop tools. The connectors your agents can discover are the connectors your managed tools receive.
New Connectors Appear Automatically
When you add a connector, or publish an existing one to the catalog again, it reaches your managed tools on their next check-in. No workstation needs any action.
Disabling a connector, or turning off Publish to endpoint catalog, removes it from managed tools on their next check-in. The Applied column of the Managed Devices dashboard confirms whether a workstation applied its MCP configuration.
Related
- Configuring Connectors — set up the connectors that expose MCP tools
- Connecting to a Gateway MCP Connector — how agents reach the MCP servers the gateway hosts, and how OAuth sign-in works
- Managed Devices — confirm which tools have applied their MCP configuration